11 regulations.
1 platform.
Instead of 11 systems, 11 consultants and 11 spreadsheets — manage ISO 27001, NIS-2, DORA, the EU AI Act, ISO 42001, TISAX, GDPR, EU whistleblowing, the CRA, BSI IT-Grundschutz and EN 9100 in a single ISMS platform. Built for mid-sized companies.
ISO 27001
Clauses 4–10 and 93 Annex A controls
NIS-2
Scope assessment, Art. 21 and reporting duties
DORA
ICT risk management, resilience testing & third-party register
EU AI Act
AI risk classification, documentation & governance
TISAX NEW
Automotive security: catalogue, scope, assessment & maturity
GDPR NEW
Records of processing, DPIA, DPAs, data-subject requests & retention policy
Whistleblowing NEW
EU Whistleblower Directive: reporting channel & case management
ISO 42001 NEW
AI management system: governance & controls
CRA NEW
SBOM, vulnerabilities & CE conformity
BSI IT-Grundschutz NEW
BSI 200-1 to 200-4, Grundschutz check
EN 9100 NEW
Configuration, first articles & supply chain
Cross-entity inference: one click — 37 entries.
Others give you wizards and templates. We auto-populate with real values from 158 curated vendor profiles. A single system click creates up to 38 linked entries across 16 inference modules — and the system’s Annex A controls go straight into your SoA. All 230 catalogue systems return suggestions — 31 entries per system on average.
- 2Asset entriesHardware + softwareCMDB
- 3RisksData loss, outage, tamperingRisk
- 1Supplier25 fields pre-filledVMS
- 1BCM processRTO/RPO definedBCM
- 5Recurring tasksBackup test, DR exerciseOps
- 1Backup registerRetention & classesGDPR
- 10Privacy-by-design checkspre-filledPbD
- 3CVE watch entriesfor Veeam componentsVuln
- 2KPI metricsBackup & recovery rateKPI
- 3TrainingOperator, admin, BCMAwareness
- 1Incident playbookBackup failure responseIR
- 1Processing recordProcessing activity pre-filledGDPR
- 1Retention classRetention period assignedGDPR
- 1Cryptography entryEncryption documentedNIS-2
- 1ICT register entryThird-party registerDORA
- 1TPRM assessmentSupplier questionnaire createdTPRM
One foundation. All eleven standards.
Our target operating model is a capability model with 111 building blocks across 10 dimensions. Every block is linked to the matching phases of all 11 standards — 589 mappings in total. Maintain evidence once and reuse it across standards.
Linked both ways: For each block you see which phase of which standard it covers — and for each standard, which blocks are already in place. Maintain evidence once, use it many times.
UI and content in English at the flick of a switch.
The whole platform — interface, 220+ standard entries, 13 reports, all training courses and demo data — is bilingual German/English throughout, with locale-aware queries in every module. Your German and English-speaking staff work in the same system, each in their own language.
Implement once — compliant 11×
ISO 27001, NIS-2, DORA, the EU AI Act, TISAX, GDPR, EU whistleblowing rules, ISO 42001, the CRA, BSI IT-Grundschutz and EN 9100 overlap heavily. Implement ISO 27001 properly and you already meet up to 80% of the other requirements. Our platform is built around exactly those synergies.
ISO 27001
- 93 Annex A controls
- Clauses 4–10
- Risk management
- SoA generator
NIS-2
- Art. 21 measures
- Reporting duties
- Business Continuity
- Supply chain security
DORA
- ICT risk management
- Resilience Testing
- Third-party register
- Incident reporting
EU AI Act
- AI risk classification
- AI system register
- Transparency obligations
- Governance framework
TISAX
- VDA-ISA catalogue
- Scope definition
- Maturity Assessment
- Prototype protection
GDPR
- Records of processing
- DPIA & technical measures
- DPA management
- Retention policy
Whistleblowing
- Internal reporting channel
- Case management
- Anonymity safeguards
- Deadline tracking
ISO 42001
- AI governance
- AI risk analysis
- Model Lifecycle
- Third-party AI
of the requirements overlap
Risk management, document control, incident management and supplier assessment — all eleven regulations ask for these. With iso-easy you implement them once and are compliant for all eleven. That saves you months of duplicated work.
A plan for every compliance requirement
Start with one standard and scale when you need to. All plans can be cancelled monthly — no minimum term.
equals 208 € / month · 2 months free
One standard all the way to certification — complete, nothing held back.
- 1 standard of your choice
- Up to 10 users
- Guided path, gap analysis & system catalogue
- AI documents + 800+ templates
- PDF export & auditor view
- Risk library & training
- Business continuity (BCM)
- No operations dashboard
- No supplier questionnaires
equals 333 € / month · 2 months free
The common case: ISO 27001 + one regulation + GDPR.
- 3 standards of your choice
- Up to 25 users
- Everything in Starter
- Operations dashboard (PDCA)
- Synchronised across standards + delta view
- Vulnerability management
- Target operating model
- Supplier & customer questionnaires
equals 499 € / month · 2 months free
For regulated businesses that have to stack several standards.
- 6 standards of your choice
- Up to 60 users
- Everything in Business
- AI adoption & agentic AI
- Benchmark & trust centre
- API & connectors
equals 833 € / month · 2 months free
+199 € / month per additional tenant
All standards, all sites — for groups and corporations.
- All 11 standards included
- Unlimited users
- Everything in Professional
- Sites & subsidiaries — each additional tenant +199 €/mo.
- SSO & priority support
- Dedicated Account Manager
- On-premises option
- Your own branding (white label)
Included in every plan
4 hours of onboarding and hands-on setup
With every order we set the platform up together with you and stay with your team until it is running — online, split across two sessions if you prefer. You never start in front of an empty system.
- 1Set-upCreate the tenant, users and roles; define the scope.
- 2Standards and gapsChoose your standards, populate the system catalogue, read the first gap analysis together.
- 3Working in the systemThe guided path, documents from templates and AI, risks, tasks and evidence.
- 4Your questionsOpen floor, handover to your team, planning the next four weeks.
All prices exclude VAT · cancel monthly
Enterprise: each additional tenant (subsidiary, site) +199 € / month
See the ISMS platform live in 30 minutes
Book a free demo or just drop us a line — we come back within 24 hours with a straight assessment of your situation.
- Reply within 24 hours
- Realistic timelines and costs
- No sales pressure, no obligation
- By notivia GmbH, Stuttgart — since 2019
See iso-easy in action
From gap analysis to the finished audit report — all in one interface.
Screenshots show the German interface — the platform switches to English at the press of a button.
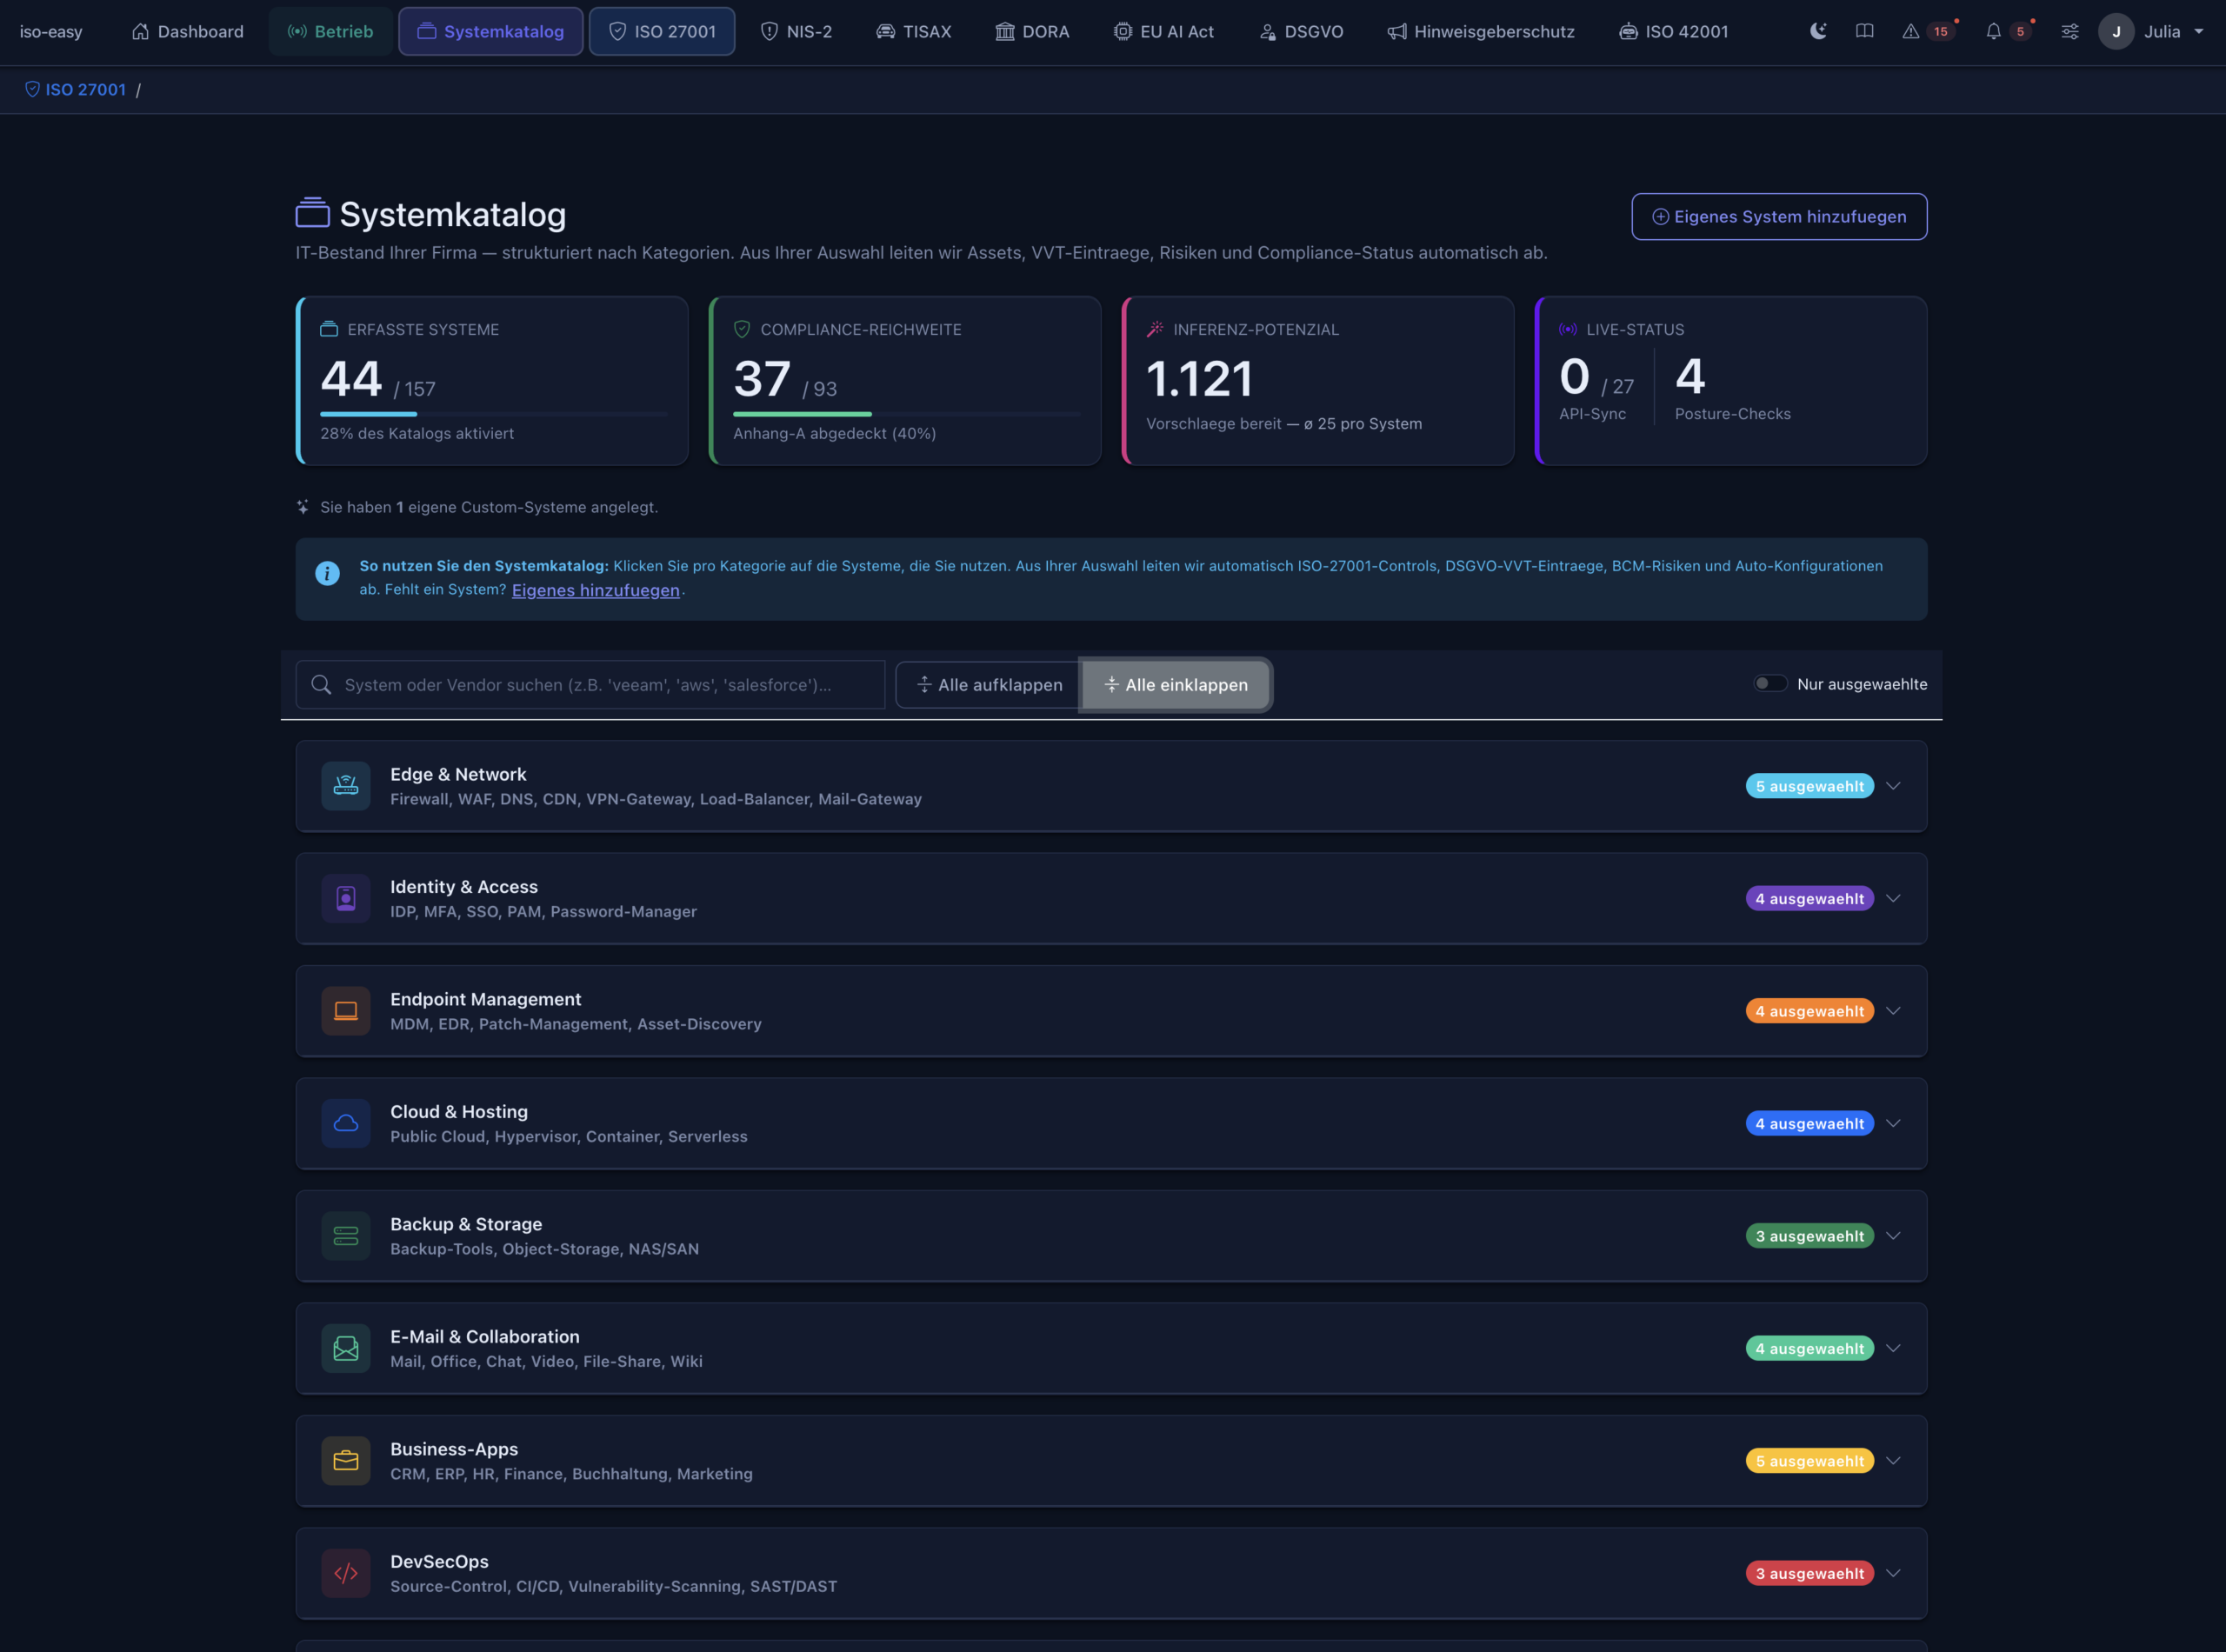
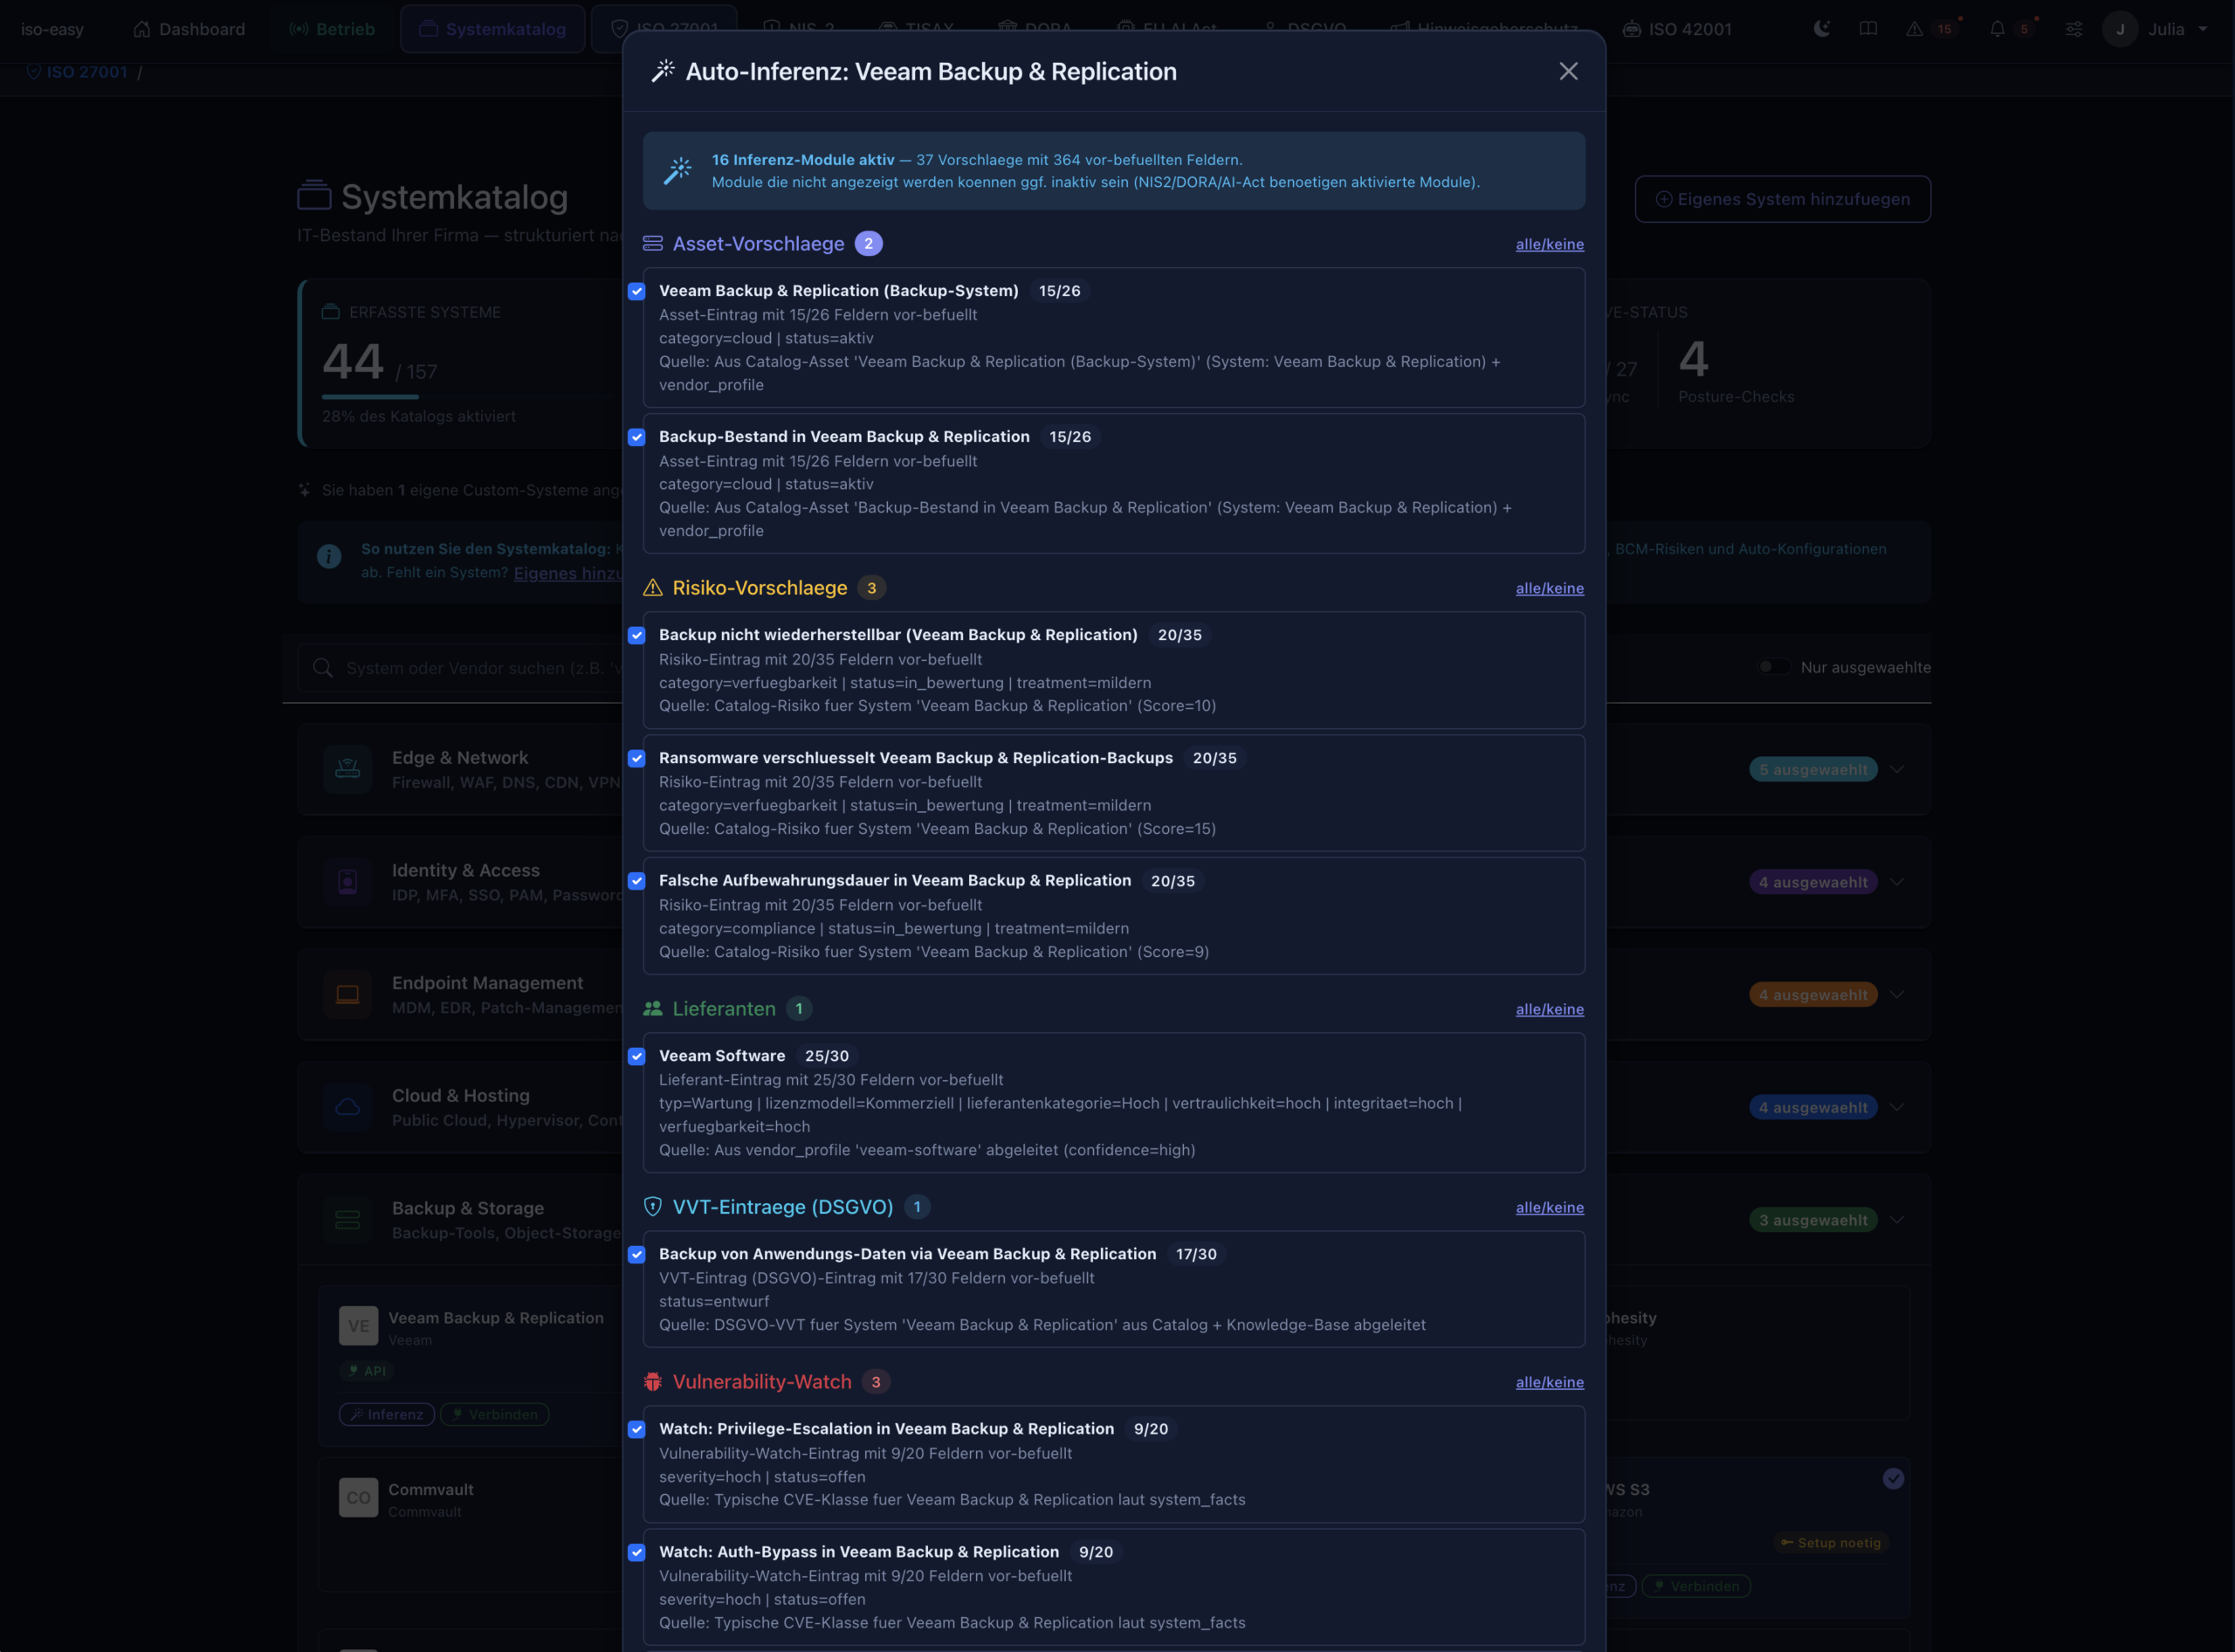
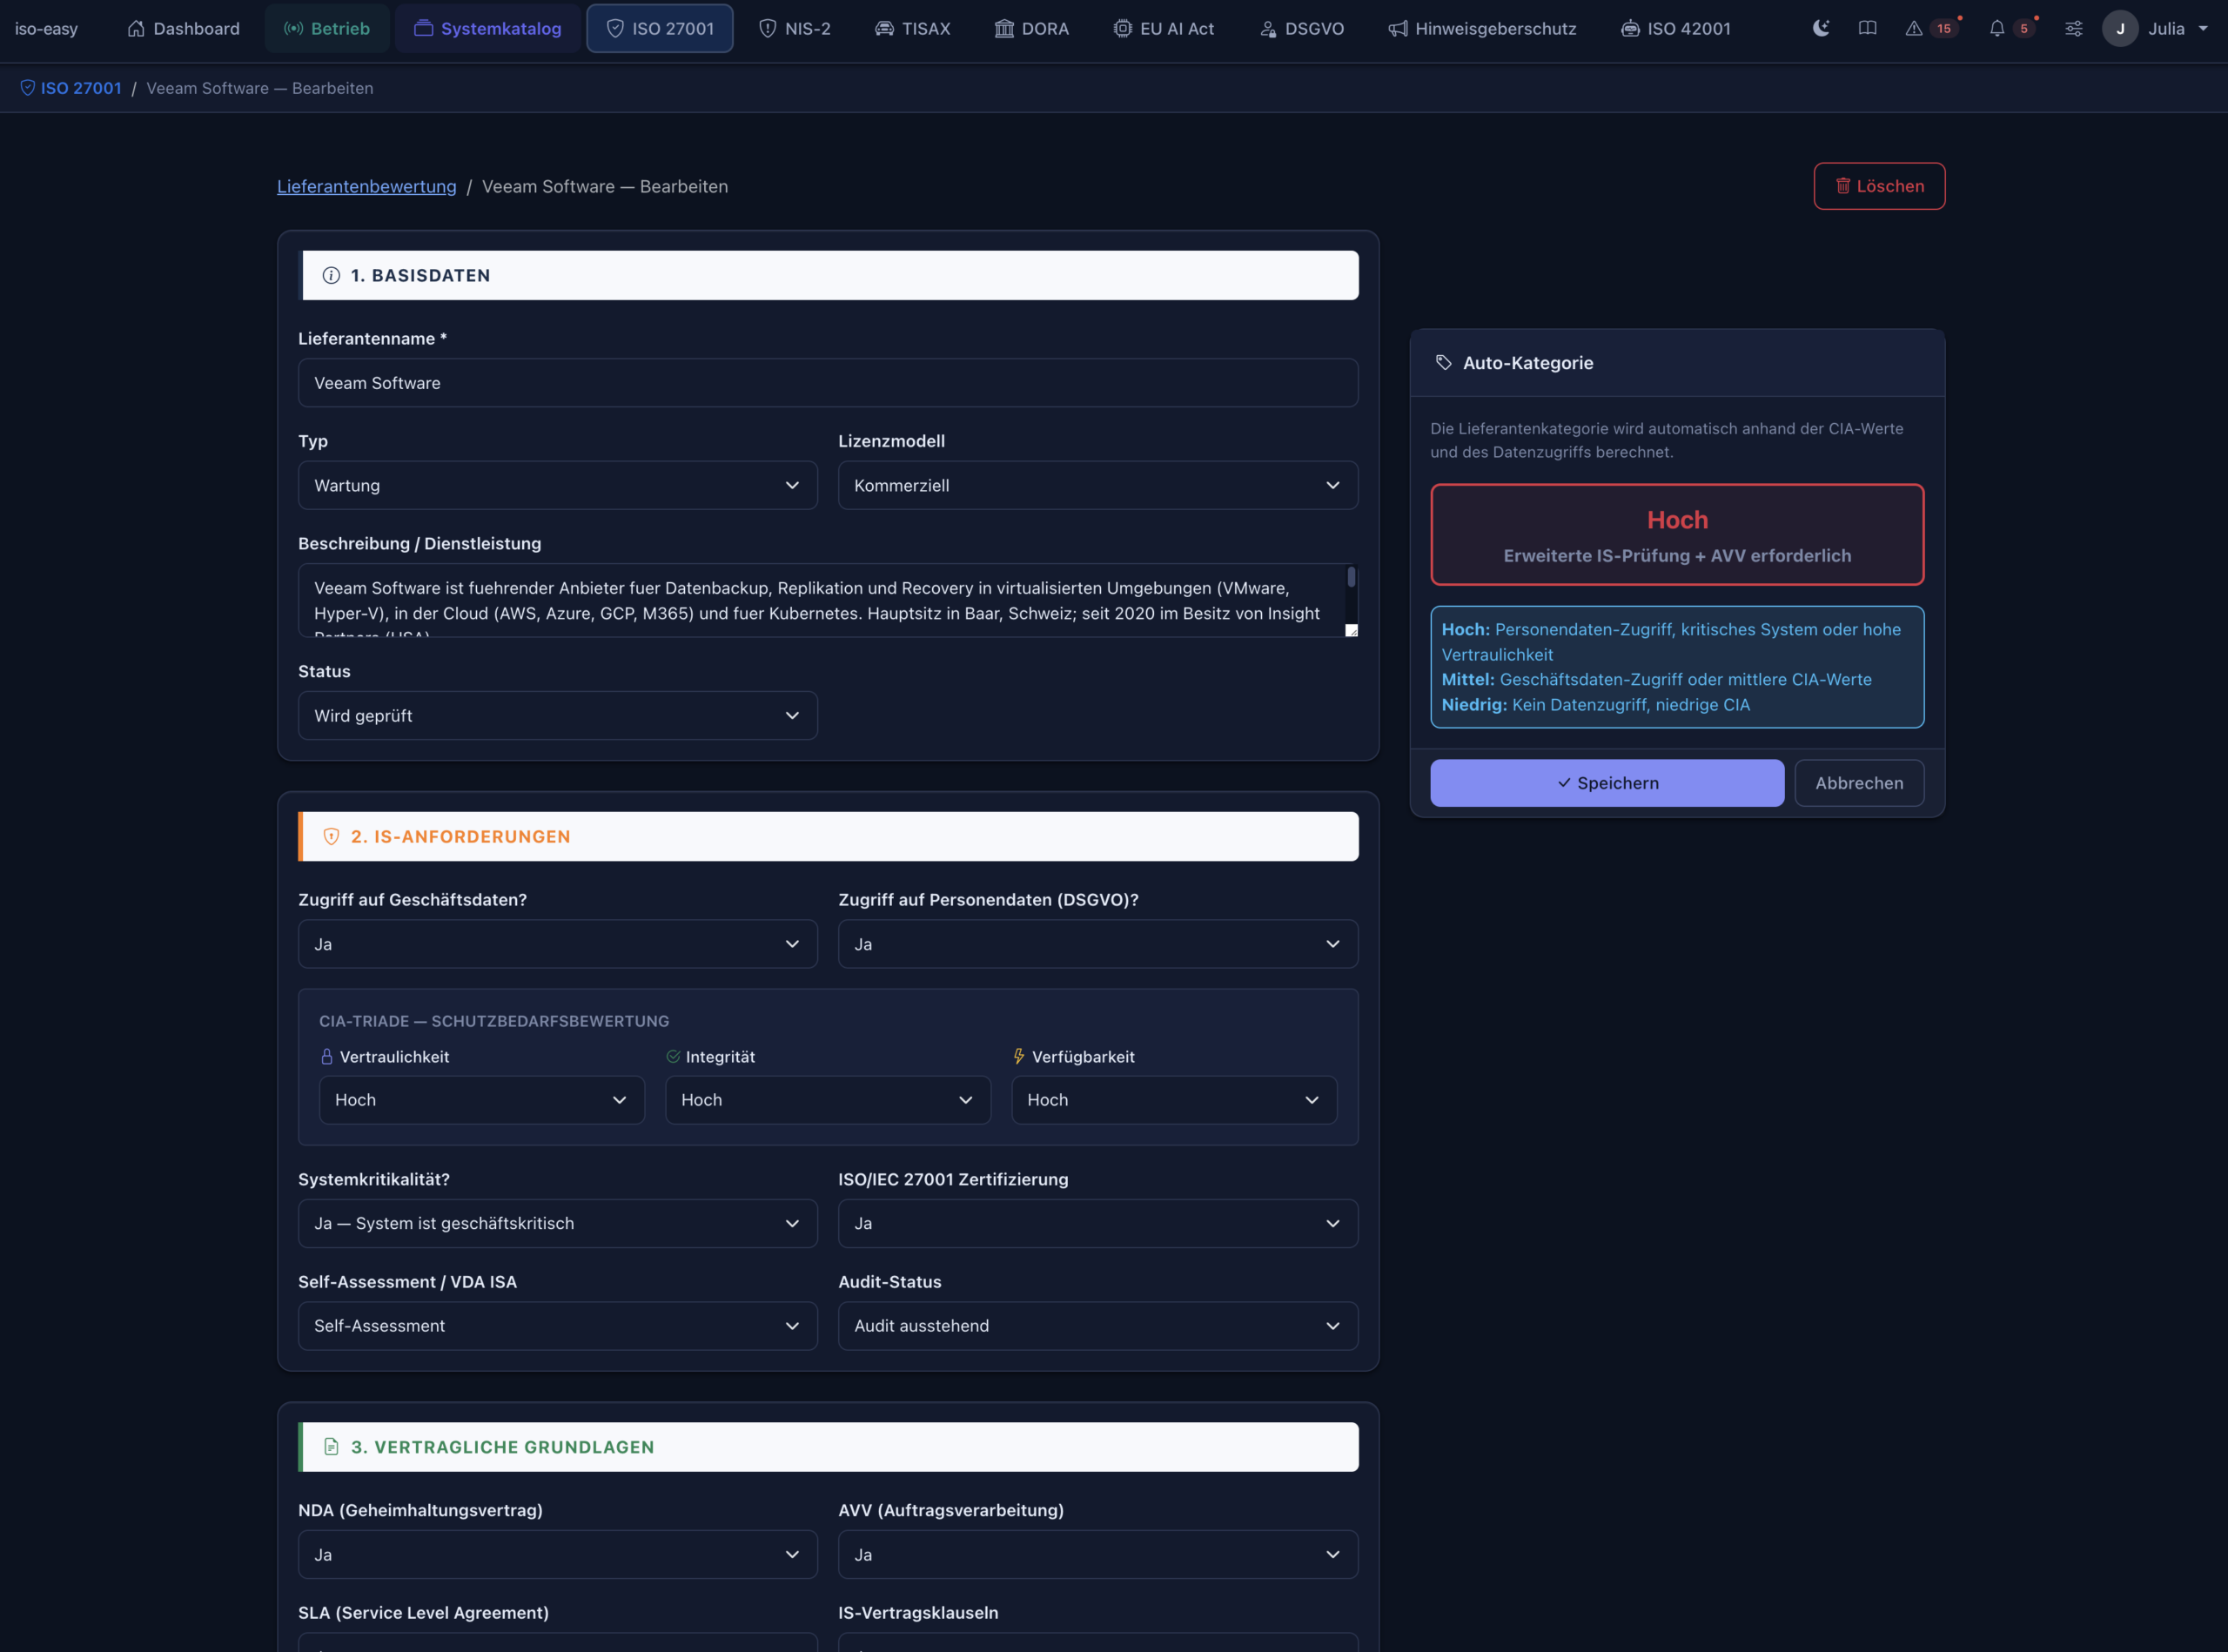
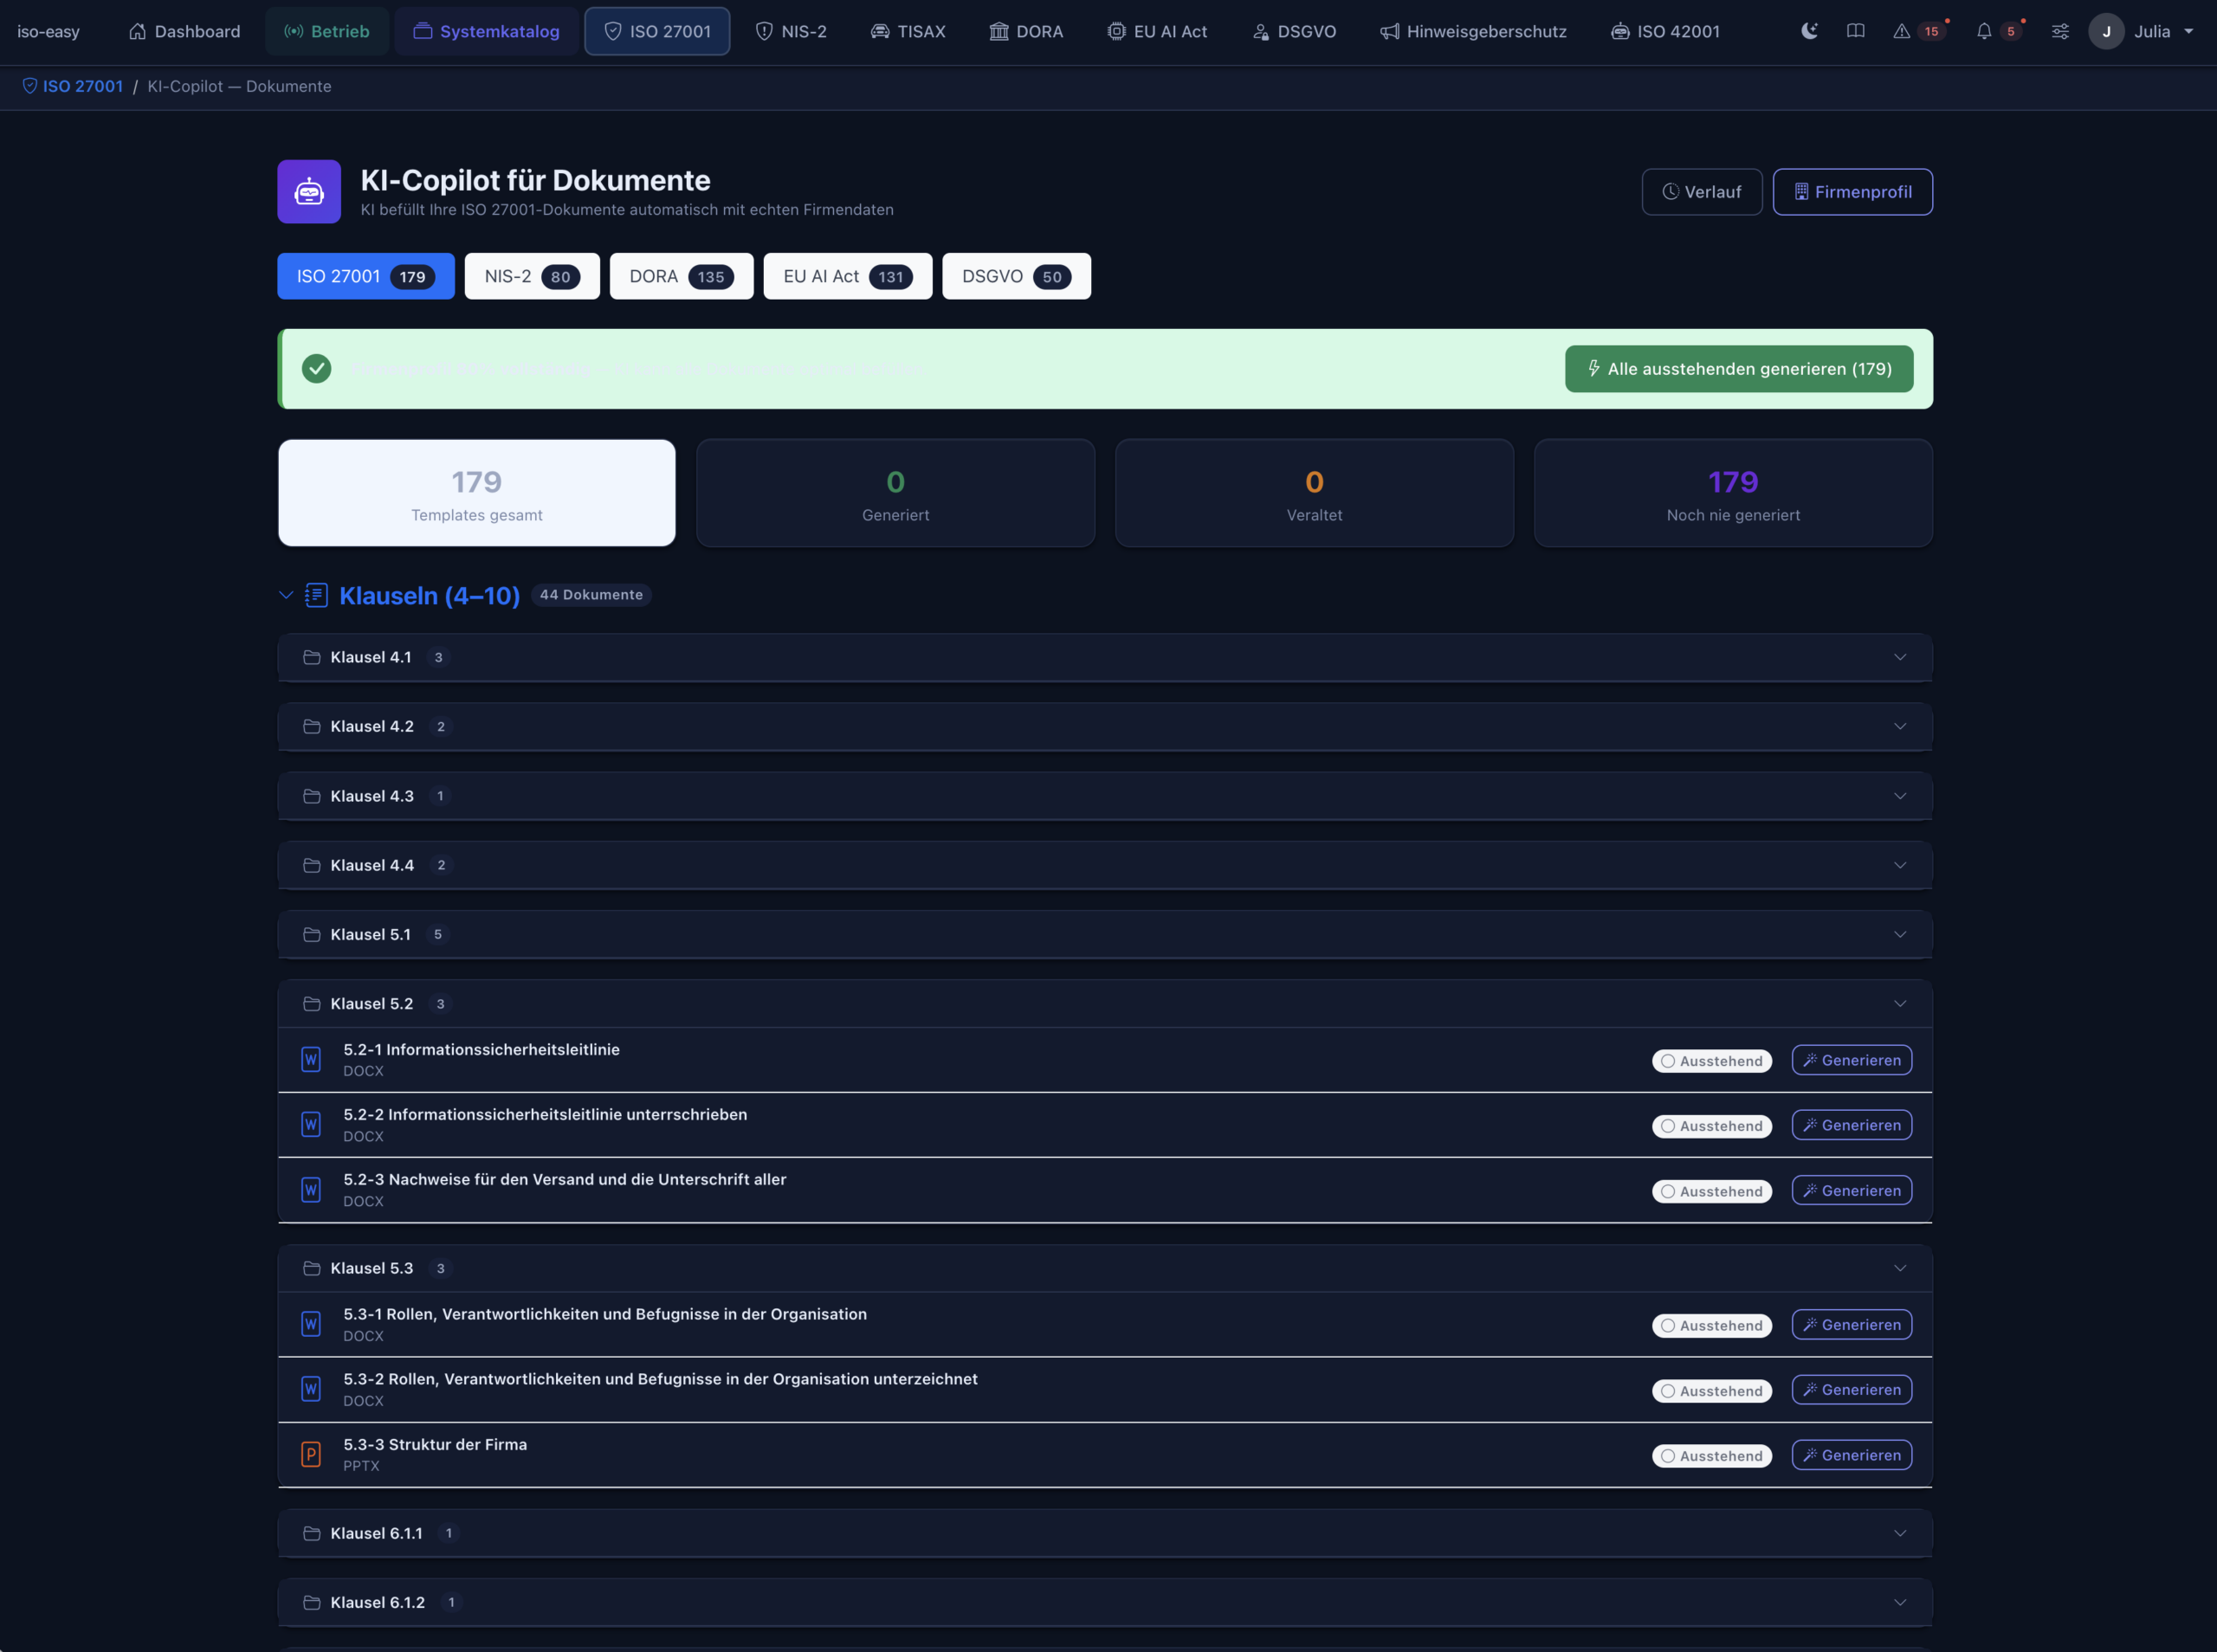
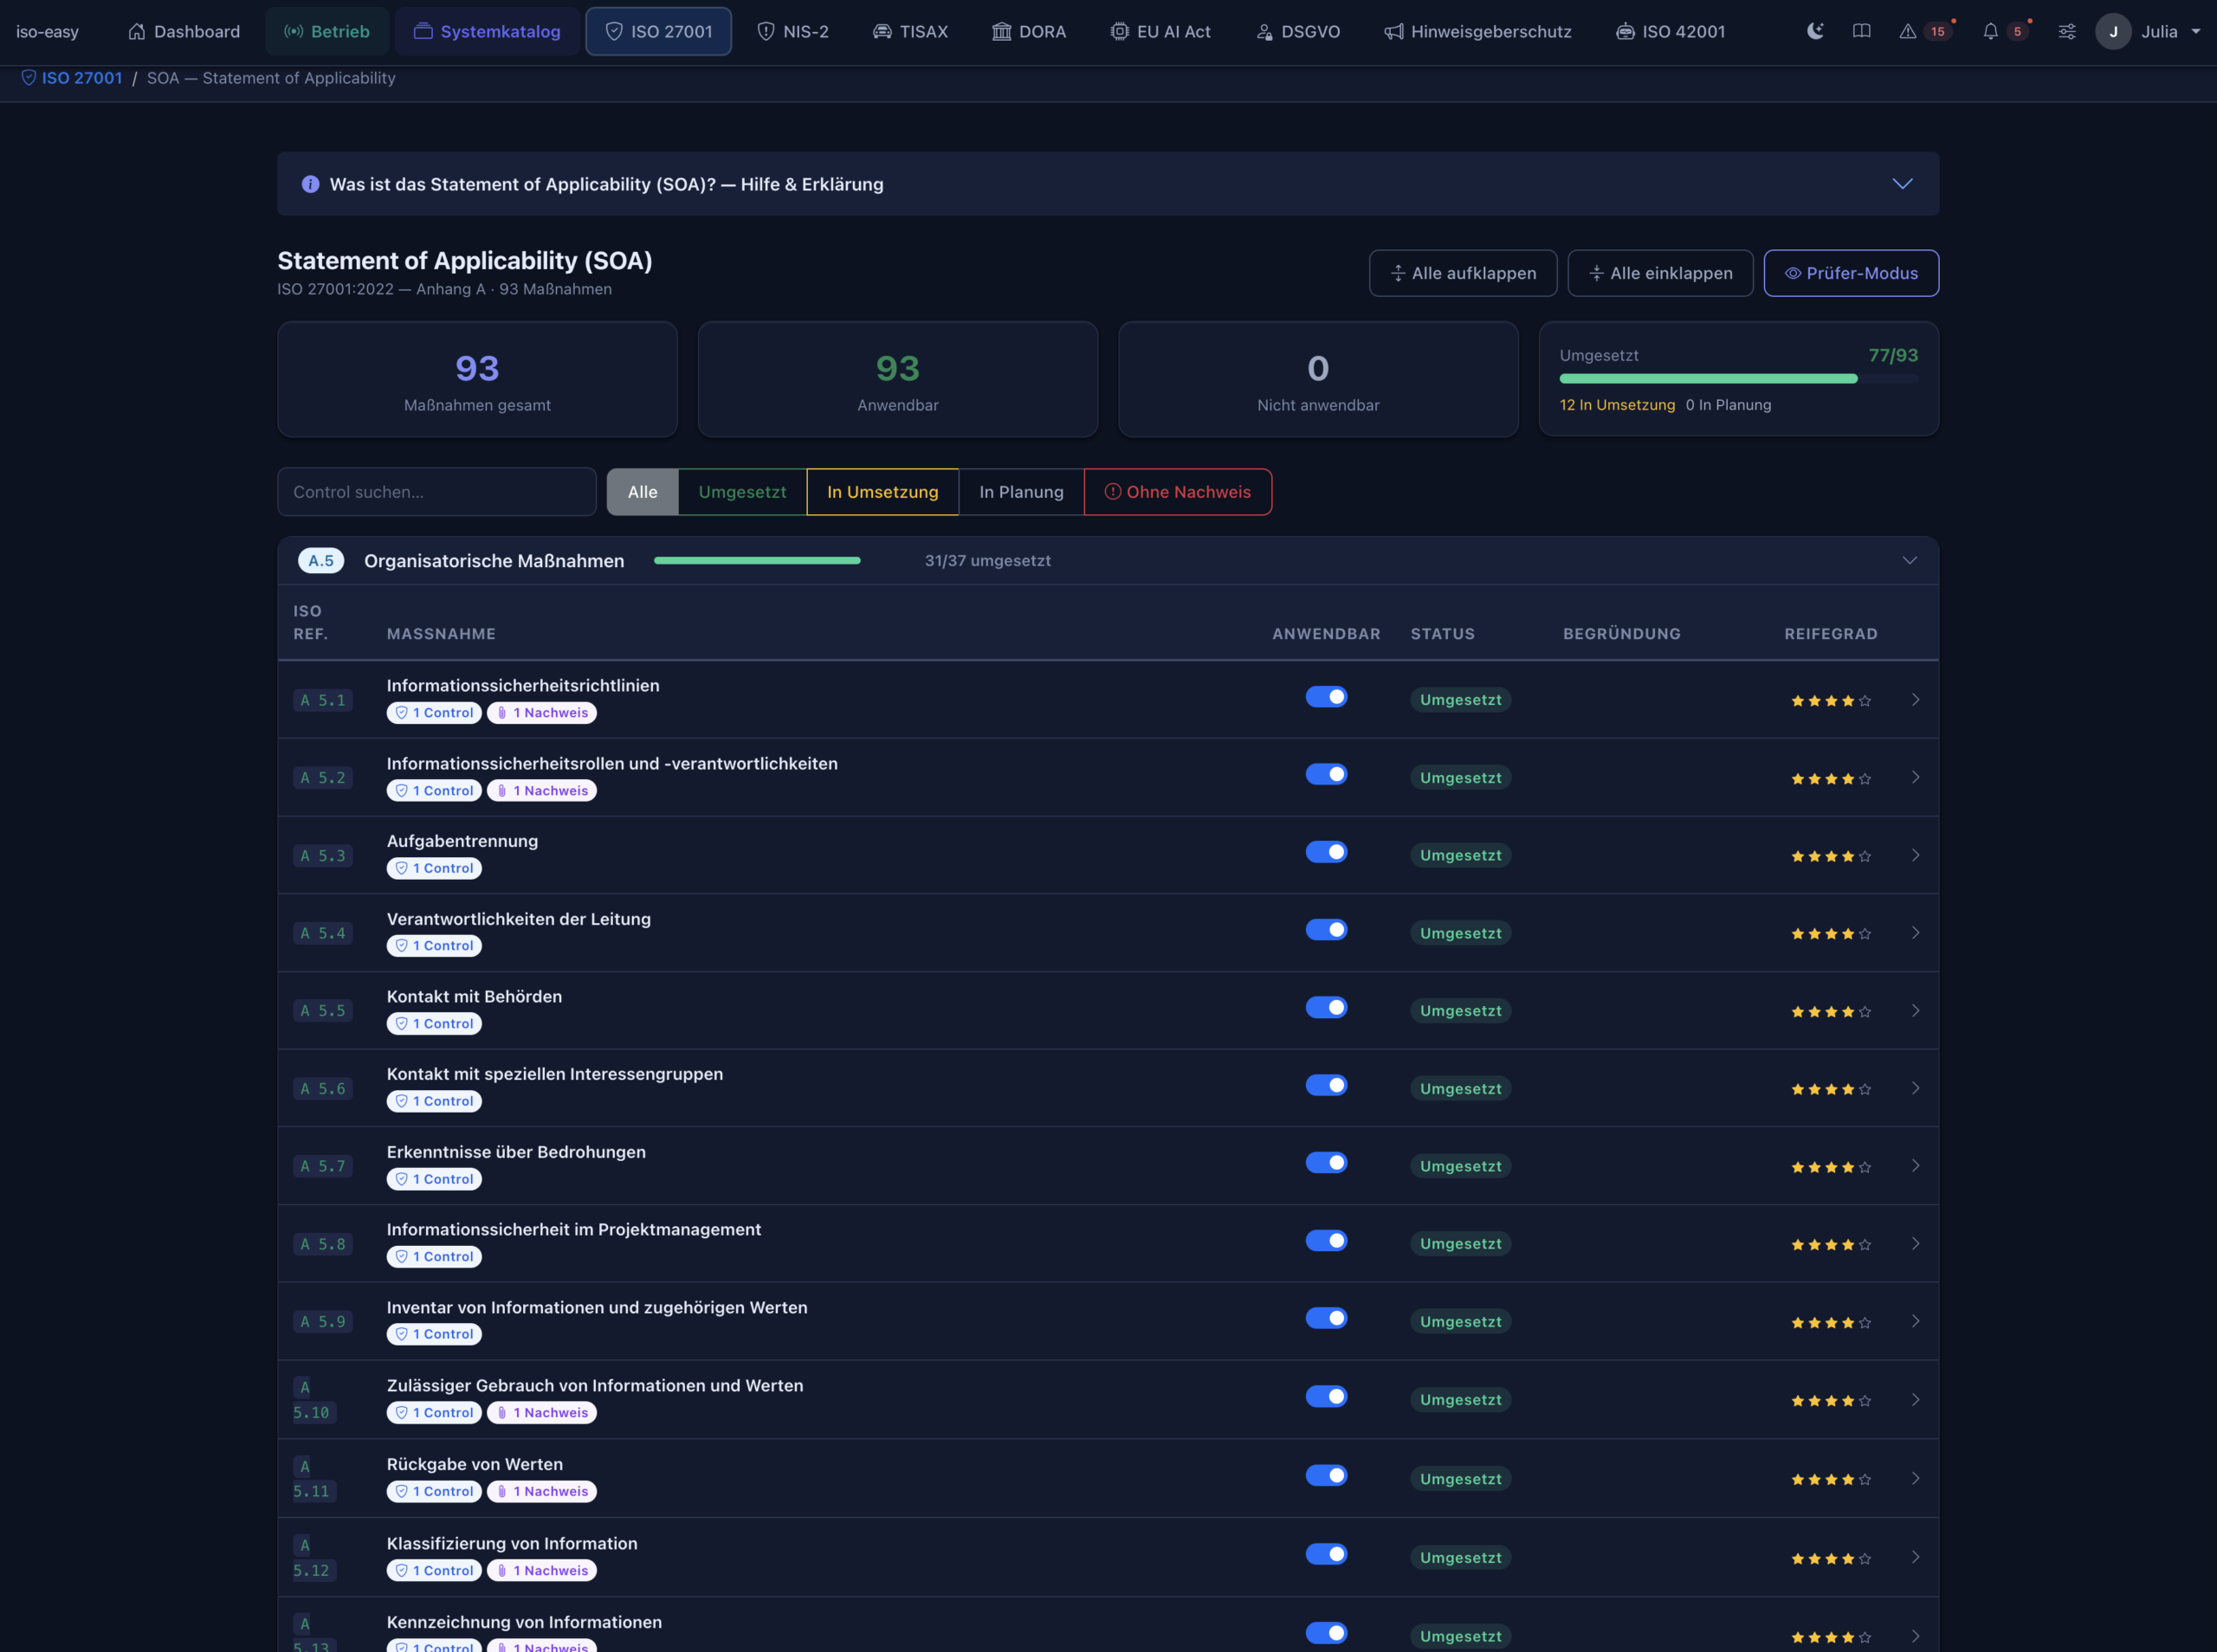
30+ modules — all in one platform
Each module stands on its own but works closely with the others. Risks link to assets, controls to tasks, documents to requirements — and everything is mapped to all eleven standards.
Core modules 8 modules
Dashboard
Compliance score, open tasks and critical risks at a glance — for all eleven standards at once.
Framework
ISO 27001 clauses 4–10, 93 Annex A controls, NIS-2 Art. 21, DORA Art. 5–15 and TISAX VDA-ISA, structured and open for comments.
Documents
AIUpload, versioning and approval workflow: draft → submitted → approved. Usable for all 11 standards.
Asset Management
Record information assets, assign CIA ratings and owners. ICT assets are classified for DORA automatically.
Risk management
AI3x3 to 5x5 risk matrix, 120 templates and treatment planning. AI-assisted risk identification for all 11 standards.
Controls
All 93 Annex A controls, cross-mapped to NIS-2 and DORA. Implementation status, evidence and due dates.
Task manager
12 ISMS swimlanes, a four-stage workflow with second-pair-of-eyes verification. Tasks are assigned to the right standard automatically.
Configuration
Manage users and roles, define business functions and adapt the platform to how you work.
AI & automation 5 modules
AI copilot
AIAI-assisted risk and control recommendations. Documents filled with your company data automatically. One-click import.
Readiness Score
Certification readiness across 6 dimensions — with separate scores for all 11 standards.
Audit guide
AINEWAI-generated audit criteria per clause and standard. Concrete tasks and live progress towards audit readiness.
AI system register
NEWRecord every AI system in your company, assign its risk class and document the EU AI Act transparency obligations.
Incident management
NEWRecord, assess and report security incidents on time. Workflows for NIS-2 (24h), DORA (4h) and ISO 27001 A.5.24–A.5.28.
Extended 5 modules
Supplier assessment
Record and assess supplier risk. Annex A 5.19, NIS-2 supply chain security and the DORA third-party register in one place.
Training records
Plan training, record attendance, upload evidence. Meets ISO 27001 cl. 7.2 and NIS-2 Art. 20.
Operations dashboard
NEWPDCA cockpit, health score, certificate countdown, logbook, risk reviews and access logs for day-to-day operation.
BCM
NEWBusiness continuity management: BIA, continuity plans, recovery times and exercise planning.
Management Review
NEWStructured management review of information security as required by cl. 9.3.
Standard-specific 6 modules
TISAX
NEWVDA-ISA catalogue, scope definition, assessment workflow and maturity tracking for the automotive sector.
GDPR
NEWRecords of processing, DPIAs, DPA management, data-subject requests, breaches and retention policy.
Whistleblower protection
NEWInternal reporting channel under the EU Whistleblower Directive: anonymous reports, case management, deadlines and feedback duties.
CRA
NEWProduct classification, Annex I requirements, SBOM and vulnerabilities, ENISA notifications and conformity assessment for CE marking.
BSI IT-Grundschutz
NEWStructure analysis, protection requirements, modelling per the BSI compendium, Grundschutz check, 200-3 risk analysis and implementation plan.
EN 9100
NEWIAQG requirements, product safety, configuration management, supply chain, first article inspection and certification preparation.
New since June 2026 8 modules
Target operating model
NEWA capability model with 111 building blocks across 10 dimensions. 589 mappings — one foundation for all 11 standards, plus BaFin and FINMA.
Multi-standard cockpit
NEWEvery standard you have booked, with a progress ring and a status light for each, in a single view.
Company profile
NEWStructured master data instead of a wall of text. Completeness indicator, and the basis for AI document generation.
Sites & group hierarchy
NEWMulti-site and group administration. Any of the 11 standards can be scoped per site.
Partner / reseller model
NEWCo-branding, hybrid billing, partner document approval including self-approval. A consulting playbook for partner tenants.
AI contract scanner AI
NEWChecks contracts automatically against GDPR, ISO, DORA and NDA clauses. Flags risks and missing mandatory clauses.
AI CVE assessment AI
NEWJudges automatically whether a CVE affects the tenant and suggests the assets concerned.
Privacy policy generator AI
NEWAI-assisted generator for GDPR-compliant privacy policies, built from platform data.
34 connector backends — Plug & Compliance
Direct API access to the systems you already run:
9 services
and 10 further backends — HashiCorp Vault, CyberArk, Snyk, Datadog, Splunk Cloud, New Relic, PagerDuty, 1Password, Pipedrive, Microsoft Purview & Sentinel.
